New Smart Sampa flaw exposed footage from 17,000 cameras, UOL reports
The vulnerability involved a company that stores video in the cloud for partners of São Paulo's surveillance program; City Hall says the list of links was never public.
Translated from the Portuguese original by the Panorama newsroom. Read in Portuguese
Summary written by the Panorama newsroom from the sources listed below. Facts are attributed to the original publications.
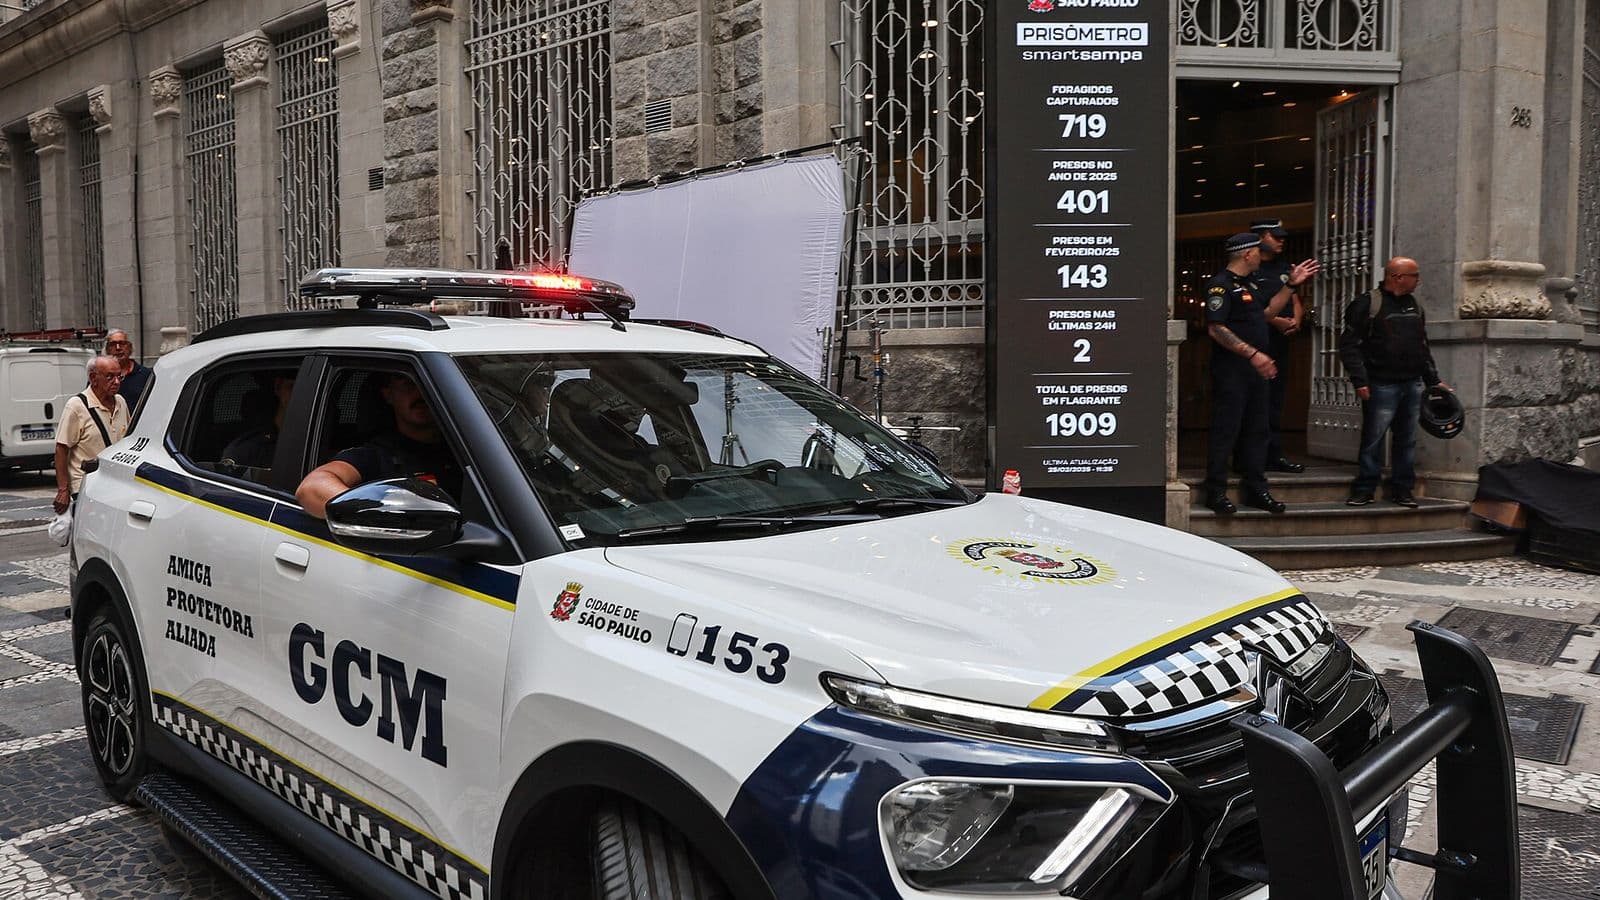
The platform of Smart Sampa, the São Paulo city government's video surveillance program with facial recognition, had a second security flaw that allowed footage from 17,000 cameras to be viewed, according to a report by UOL columnist Artur Rodrigues, picked up by Folha de S.Paulo on Tuesday (Nov. 3).
According to UOL, the vulnerability involved cameras hosted by Monuv, a company that provides cloud storage to the program's partners, and the feeds could be accessed directly for five days. As proof, the columnist waved at cameras in the city center and later retrieved the footage. He said he saw streets where officials live, such as Supreme Federal Court (STF) Justice Alexandre de Moraes and former presidents Michel Temer and Fernando Henrique Cardoso.
The first flaw, revealed by UOL on Oct. 20, involved possible unauthorized access to 89,000 cameras. Folha also reported, based on technical documents and accounts from cybersecurity experts, that flaws in the SentinelX platform, on which the program is built, left web addresses and data linked to several municipalities exposed.
City Hall said the list of links "was never public" and that there are no signs of an attack on the system. The Municipal Urban Security Department said the spreadsheet resulted from a cybersecurity review carried out by Prodam, the city's technology company, at the request of Mayor Ricardo Nunes, and that sending the file to UOL constitutes a new criminal leak, and that steps will be taken to investigate and hold those involved accountable.
Monuv said it follows good security practices and the specifications set by Smart Sampa itself, and attributed the exposure of the links to the leak of access credentials on the program's platform.